

Two quiet moves in September 2026 answered the same question. On 9 September, Shopify bought Tailwind Labs, whose framework is installed over 110 million times a week, and kept the code MIT-licensed. The Django Software Foundation hired its first paid Executive Director, bankrolled by $47,500 from six agencies. One project was bought outright; the other, supported. Both respond to one fact: roughly 60% of open source maintainers still earn nothing from the code the world runs on.
This page is that reckoning explained, not a how-to: why free code keeps winning while maintainers go unpaid, which models could change that, and how to judge your dependencies. It stays at what and why, pointing to the deep-dives.
In This Series
- Why free open source always wins and who really pays for it: why free code wins and nobody must pay maintainers.
- How acquisition, foundations and registry royalties could fund open source: the three resolutions for closing the gap.
- How AI slop, maintainer burnout and the xz backdoor broke open source: the AI-driven surge in maintenance load.
- How to assess the funding and governance risk of a critical dependency: a frame for reading bus factor, funding and governance.
What is the open source funding and governance reckoning of 2026?
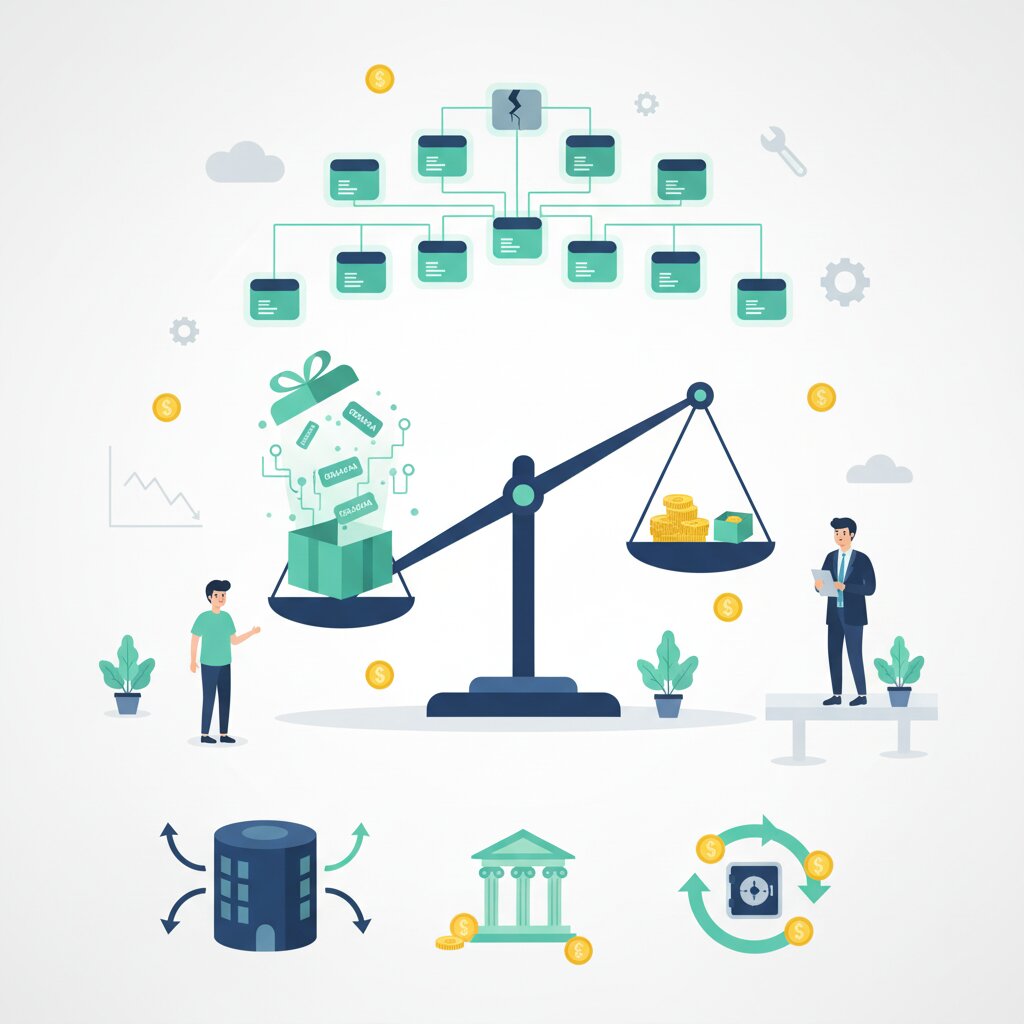
The reckoning is the moment a decades-old arrangement — companies consume free code while its maintainers go unpaid — is finally being rewritten. About 60% of maintainers earn nothing, a figure flat since 2021, even as that labour generates billions. Through acquisitions, foundations, regulation and proposed registry royalties, the industry is now deciding who pays, who governs, and what sustainable really means.
Three concepts carry it: the free-code equilibrium (free code wins because a copy’s marginal cost is zero), the funding gap (value extracted far exceeds money returned) and corporate patronage, the voluntary default that is failing.
Why 2026? Three forces matured at once: the economics, the AI-driven maintenance surge, and a supply-chain near-miss in the xz utils backdoor. How you respond is a fourth. For the deepest definition, start with why free code always wins over paid alternatives.
Why does free code always win — and who really pays for it?
Free code wins because its copies cost nothing to distribute, so the market price clears at exactly zero. The corollary is that the labour behind free code has no natural revenue line: you pay for guaranteed, scanned supply from JFrog or Docker, while the maintainer is rarely paid. Understanding this equilibrium is the key to judging every proposed funding fix.
The zero-cost fallacy is the finance-side misread that turns a $0 download into a $0 total cost, hiding maintainer labour. The asymmetry in one line: GitHub Sponsors has moved $100 million since 2019, against JFrog’s $532 million in 2025. The split runs two ways: patronage (GitHub Sponsors) versus public programmes like the Sovereign Tech Fund.
Licensing has not produced maintainer income. The MIT/Apache versus GPL debate misses the point, and relicensing attempts each lost to a fork: Elastic to OpenSearch, HashiCorp to OpenTofu, Redis to Valkey. The full economics is in why free code always wins. The AI surge straining that equilibrium, and the three resolutions, get their own sections.
How could acquisition, foundations and registry royalties fund open source?
Three models compete to close the gap. Each answers who pays, who governs and whether the fix lasts. Acquisition buys a maintainer outright, as with Shopify and Tailwind: stability for the code, no guarantee for the commons. Foundation stewardship gives a project a neutral, funded home, like the Django role or the Linux Foundation. Registry royalties place a small levy where distribution happens — npm, Docker Hub or Maven Central — and pool it back to maintainers.
The split that matters is charity versus mandate: patronage is reversible, a levy or funded foundation role closer to a mandate. The trade-offs stay open: acquisition rescues one codebase but not the commons, a foundation can de-risk governance without funding maintainers, and royalties are untested on rate-setting and audit. Compare them in the three funding models compared.
How did AI slop, maintainer burnout and the xz backdoor break open source?
AI made it cheaper to generate bug reports and code than to review or maintain them, flooding maintainers with noise while genuine signal shrank. curl shut its $90,000 bug bounty when real reports fell from 15% to under 5%. That load lands on people who are already unpaid, and the xz utils backdoor showed how an exhausted solo maintainer becomes a soft target. The threat is human, not technical.
The picture is not one-sided: Google’s Big Sleep and Anthropic’s work with Mozilla on libxml2 found genuine bugs, so AI is both cause and cure. The xz utils backdoor made it concrete: a solo maintainer, Lasse Collin, was worn down by sustained pressure, and the backdoor was caught by luck, not process, when Andres Freund noticed a 500-millisecond delay in SSH logins.
The full account is in the AI-driven maintenance crisis; the funding gap behind burnout is the economics above, your bus factor the due-diligence below.
How do you assess the funding and governance risk of a critical dependency?
You judge a dependency like any supplier you can’t easily replace: who actually maintains it day to day, whether they’re paid and resourced, and what happens if they leave. The signals that matter are maintainer concentration, funding model, governance and continuity — not commit count. A foundation home can de-risk governance without solving funding, and fork-versus-fund is a judgement, not a procedure.
The first signal is the dependency footprint, mapped via an SBOM. A busy commit cadence is not the same as maintenance: depth, issue backlog shape, release recency and who actually merges matter more. Bus factor is the shorthand worth keeping — how many people could cut an emergency release tomorrow.
Two scorers help: the OpenSSF Criticality Score and the OpenSSF Scorecard, both with traps: Goodhart’s Law (gaming what is measured) and the Streetlight Effect (measuring what is easy over what matters). Forking can double your own bus factor, though you inherit the maintenance. CISA guidance and the EU Cyber Resilience Act turn this from preference into obligation. The practical frame is in assessing your own dependency risk.
Resource Hub: The open source funding and governance reckoning — deep dives
Understanding the reckoning
- Why free open source always wins and who really pays for it — why the zero marginal cost of a copy clears the price at zero, and why $100M in sponsorship is a rounding error against the value extracted (6 min read).
- How AI slop, maintainer burnout and the xz backdoor broke open source — how AI-generated reports swamp reviewers, and how an exhausted solo maintainer became the xz backdoor’s soft target (5 min read).
The emerging resolutions
- How acquisition, foundations and registry royalties could fund open source — the three competing models, compared by who pays, who governs, and whether the fix is structural or one-off (5 min read).
From awareness to action
- How to assess the funding and governance risk of a critical dependency — how to read a critical dependency’s bus factor, funding and governance before it becomes a board-level surprise (5 min read).
Suggested reading order: the economics spine, then the pressure article, the resolutions, then your exposure.
Where to start
Open source is stable, not collapsing, which is exactly why maintainers stay unpaid. What changed in 2026 is the funding and governance layer becoming a board-level question.
Where you go next depends on the question.
- If you want the economics, start with the economics of free code.
- If you’re choosing a funding model, go to the acquisition, foundation and royalty models.
- If you own a dependency tree, skip to assessing a critical dependency’s risk.
Frequently Asked Questions
Is it true that 60% of open source maintainers are unpaid?
Yes. Roughly 60% of maintainers earn nothing for their work, and that figure has been flat since 2021 even as the code they steward generates billions. Most are volunteers fitting maintenance around a day job. The number matters because it is the gap the entire reckoning is trying to close. GitHub Sponsors has moved $100M since 2019, which sounds large until you compare it to one distributor’s $532M year.
What is a bus factor, and why does it matter?
A bus factor is the number of maintainers who could disappear before a project stalls. A bus factor of one means a single unpaid person holds the whole thing up, which is exactly what happened with xz utils. It matters more than commit count, because a thousand commits from one exhausted volunteer is still a single point of failure. Check who merges, not how much gets merged.
What happens to my software if a critical maintainer walks away?
In the short term, often nothing, because the code keeps running and forks keep building. The risk is quieter: security fixes stall, releases stop, and abandoned issues pile up. A dependency does not need to break to become dangerous. This is why continuity, who could pick it up and under what governance, is a signal worth reading before you need it.
How do I find out who actually maintains the open source I depend on?
Start by mapping what you actually run, which is what an SBOM is for, then trace each dependency to its maintainers and funding model. Look at who merges pull requests, not just who has commit access. A project with a foundation home and a funded maintainer reads very differently from one held up by a single volunteer. The full frame is in assessing your own dependency risk.
What is an SBOM, and do I need one?
An SBOM, or software bill of materials, is a machine-readable list of every component inside your software. You need one because you cannot assess a dependency you cannot see. It is the first step in judging supply-chain risk: map the tree, then read each branch for maintainer concentration, funding and governance. CISA and the EU Cyber Resilience Act are pushing this from good practice toward obligation.
Are OpenSSF scores a reliable way to judge a dependency?
They are useful starting points, not verdicts. The Criticality Score and Scorecard both measure proxies, which invites Goodhart’s Law (once a measure becomes a target, it stops measuring) and the Streetlight Effect (looking where the light is rather than where the keys are). Use them to prioritise attention, then verify what they miss: who actually maintains the project and whether that person is resourced.
Could the xz backdoor happen again?
Yes. The xz backdoor was caught by luck, not process, when Andres Freund noticed a 500-millisecond delay. Nothing structural has changed that would guarantee a different outcome. As long as critical infrastructure rests on exhausted, unpaid maintainers, a patient attacker has a soft target. Funding and governance reform is the real defence, because the threat is human, not technical.
Why did relicensing projects like Redis and HashiCorp fail?
They did not fail commercially, they failed to prevent a fork. When Redis moved off its open licence, Valkey emerged; HashiCorp’s change produced OpenTofu, and Elastic’s produced OpenSearch. Free code’s marginal cost is zero, so any restrictive licence can be forked by a competitor willing to fund it. Relicensing has never paid a maintainer’s rent.
Should I stop relying on free open source and pay for commercial support instead?
No, that misreads the problem. You already pay for guaranteed, scanned supply from vendors like JFrog and Docker, while the maintainer upstream often sees nothing. Fork-versus-fund is a judgement, not a procedure, and abandoning free code solves nothing. The better move is to direct some of that spend toward the projects you actually depend on, whether through a foundation or a levy.
How would registry royalties actually work?
A registry royalty is a small levy applied where distribution already happens, at places like npm, Docker Hub or Maven Central. The fee is pooled and routed back to the maintainers whose packages move through it. It is attractive because it follows the money to where code is downloaded, turning a voluntary donation into something closer to a mandate. The open question is who sets and enforces it.
How much would it cost to properly fund my dependencies?
Far less than most teams assume. The funding gap is about concentration, not total volume: a handful of critical packages are held up by one or two people, so targeted support goes a long way. Compare GitHub Sponsors’ $100M since 2019 against the value extracted. Start with your bus-factor-one dependencies, then decide whether to fork, fund or accept the risk.
Is open source about to collapse?
No. Open source is not collapsing, it is stable, which is precisely why maintainers stay unpaid. The equilibrium that keeps code free also keeps the labour invisible and unfunded. What changed in 2026 is not the software but the funding and governance layer around it becoming a board-level question. The reckoning is about who pays, not whether the code survives.